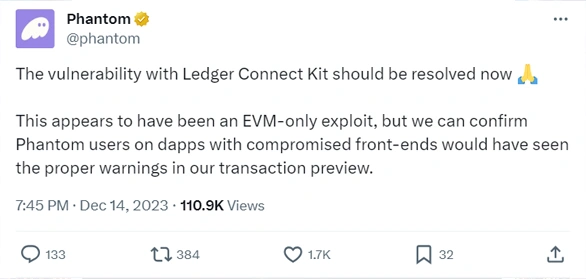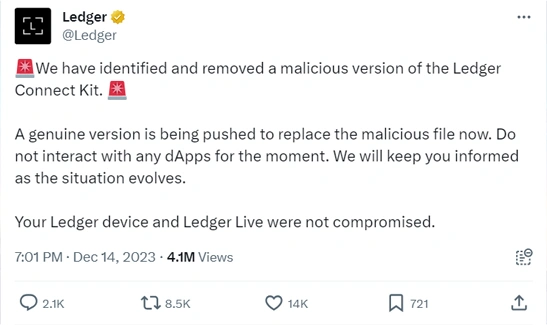
Multiple decentralized applications, such as Revoke. cash and SushiSwap, which used Ledger’s connector library have been compromised. Ledger says they’ve resolved the problem.
Ledger says they’ve resolved the problem
On December 14, there was a hack on the front end of several DApps (decentralized applications) that used Ledger’s connector, such as Revoke. cash, Phantom, SushiSwap, Balancer, and Zapper. Ledger stated that at 1:35 PM UTC, the malicious version of the file had been replaced with its legitimate version, almost three hours after the security breach was detected.
Ledger advises users “to always Clear Sign” transactions and stresses that the addresses and data shown on the Ledger screen are the only accurate sources of information. “Stop that transaction right away if the screen on your Ledger device and the screen on your computer or phone differ.”
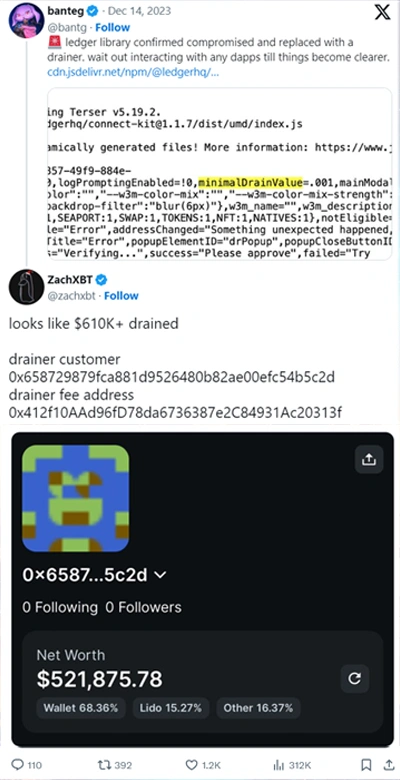
SushiSwap chief technical officer Matthew Lilley was among the first to report the problem, pointing out that a widely used Web3 connector had been compromised, allowing malicious code to be injected into a variety of DApps. According to the on-chain analyst, the compromise was confirmed by the Ledger library, where the vulnerable code inserted the drainer account address.
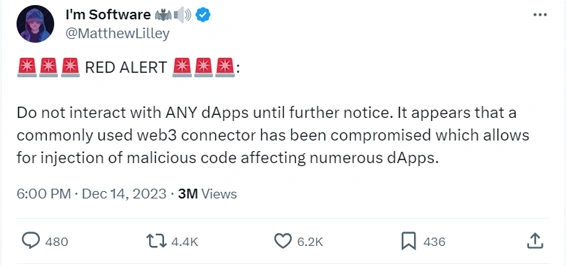
Source: I’m Software
Lilley held Ledger responsible for the ongoing vulnerability and compromise of multiple DApps. According to the executive, Ledger’s content delivery network was compromised, and JavaScript was loaded from the compromised network.
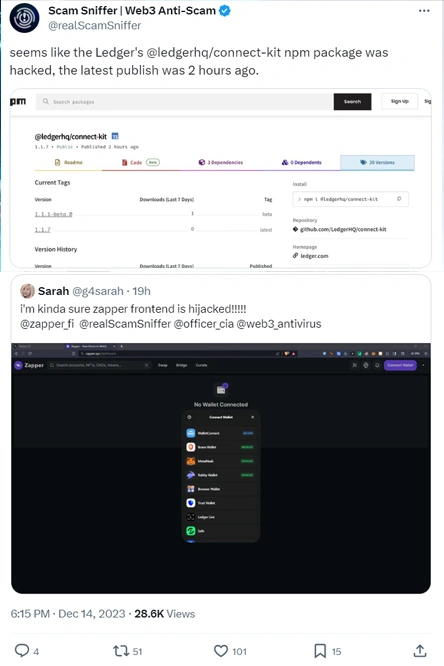
Source: Scam Sniffer | Web3 Anti-Scam
Ledger connector is a library maintained by a Ledger that is used by many DApps. Because a wallet drainer has been added, assets from a user’s account may not drain on their own. However, prompts from a browser wallet such as MetaMask will appear, potentially giving malicious actors access to the assets.