


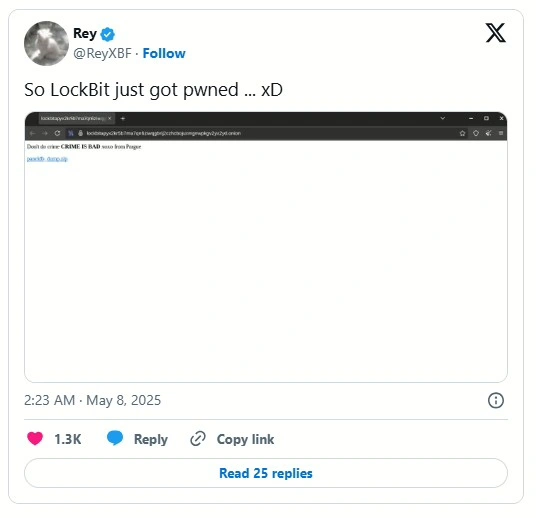
The LockBit ransomware group’s infrastructure, nearly 60,000 Bitcoin addresses associated with their operations, were exposed following a hack of their dark web affiliate panel. The leak included a MySQL database dump containing critical information such as ransomware builds, victim negotiation chats, and targeted companies. While no private keys were compromised, the exposed data offers valuable insights for blockchain analysts to trace illicit financial flows linked to the group.
LockBit, operating under a ransomware-as-a-service model, has been responsible for over 2,000 attacks globally, extorting victims for more than $120 million. The group’s affiliates used unique Bitcoin addresses for each victim, facilitating tracking of ransom payments and potentially linking them to known wallets. This exposure could aid law enforcement and blockchain investigators in identifying and disrupting the group’s financial networks.
The breach also highlighted the vulnerability of ransomware groups to counterattacks. The hackers responsible for the LockBit breach left a message mocking the group’s criminal activities, underscoring the ongoing battle between cybercriminals and ethical hackers. This incident highlights the dynamic and aggressive character of the cybersecurity field.
Get the weekly commit
New blockchain deep dives every week.
